Aider's new CVE runs through shell=True lines Aider wrote itself
SummaryCVE-2026-115726 lets a cloned repo run shell commands on anyone who starts the Aider coding agent inside it. We read the git history: both shell=True calls the exploit goes through were authored by Aider. The real bug is that nobody asked who controls the string.
· MODEL Editors · 3 min read
Some links may be affiliate links. Disclosure
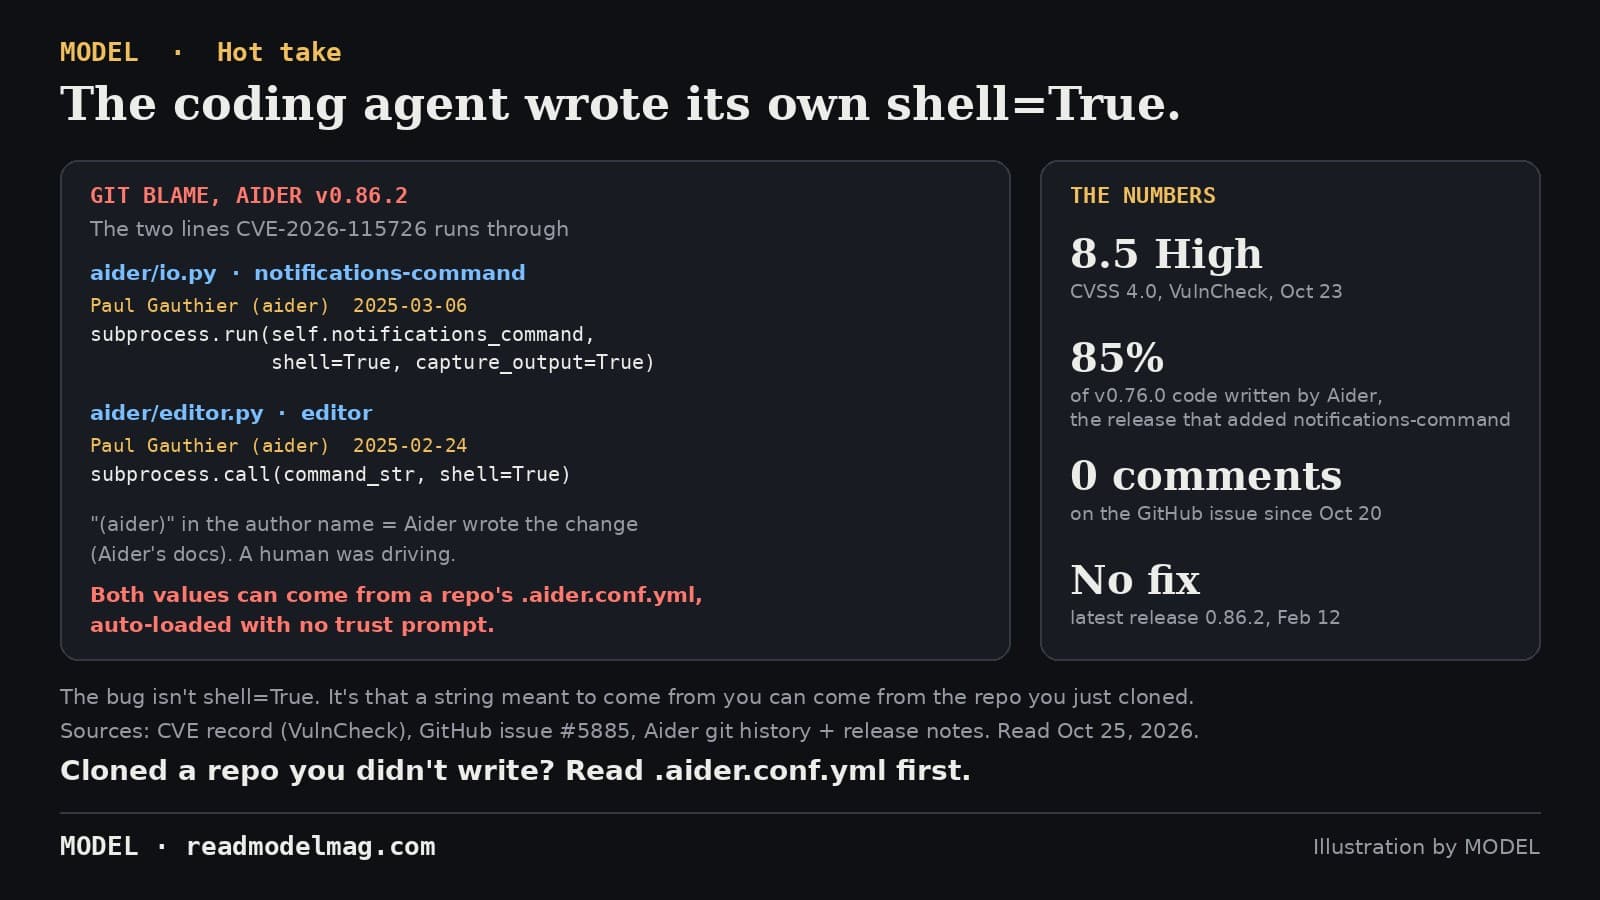
On October 23, VulnCheck published CVE-2026-115726 (opens in a new tab) against Aider, the open-source terminal coding agent (about 49,700 GitHub stars). It is rated 8.5 High on CVSS 4.0 and affects every version through 0.86.2, the latest release. Researcher Seoyoung Lee is credited with the find. The report went up as a public GitHub issue, #5885 (opens in a new tab), on October 20. As of Sunday afternoon it is still open, with no comments, no assignee and no linked fix.
How it works. Aider reads a file called .aider.conf.yml from your current folder, the git repository root and your home folder, and every command-line flag is also a valid key in that file. There is no trust prompt. Two of those keys hold commands. notifications-command is run through subprocess.run(..., shell=True) after the model replies, so once a malicious repo also sets notifications: true, the command fires on your next prompt and every turn after that. editor is passed to subprocess.call(..., shell=True) when you type /editor. Neither goes through the confirmation step Aider uses for shell commands the model suggests. Clone the wrong repo, start Aider, send one message: the repo's command runs as you.
Who wrote those lines. We read Aider's git history at the v0.86.2 tag. Aider's own docs (opens in a new tab) say that when Aider authors a change, "(aider)" is appended to the git author name. git blame on both sinks:
- The
notifications-commandfeature landed in commit65e059a7, "feat: Add notifications-command option to run custom notification commands," March 6, 2025, authored by "Paul Gauthier (aider)." Thesubprocess.run(..., shell=True)lines blame to the same author, same day. It shipped in v0.76.0, whose release notes say "Aider wrote 85% of the code in this release." - The editor's
subprocess.call(command_str, shell=True)line comes from commit3714d554, February 24, 2025, also authored by "Paul Gauthier (aider)." It replaced a line carrying a human comment:# why does adding shell=True launch the editor without the filepath? ai?
To be fair about that second one: Aider's version quoted each part of the editor command with shlex.quote. About an hour later, a commit by Paul Gauthier, without the "(aider)" tag, simplified the function and dropped the quoting, so the configured value now goes to the shell as is. Human and agent each did half of it.
Our take
shell=True on a command the user typed is the feature, not the bug. Letting people run their own notification script is reasonable. The bug is that the same value can come from a file inside a repository someone else wrote, and nothing in the code, the commit or the review asked where the string comes from.
That's the kind of question a coding agent rarely asks, because the answer isn't in the diff. The commit did what its message says: it made notifications configurable. Whether the config file is trusted input was decided somewhere else, in how Aider loads its settings. When an agent writes most of a release, one feature request at a time, trust boundaries are the part nobody is asked to look at.
The other half is maintenance. Aider's last commit to its main branch was May 22, 2026, and its last release was February 12. A coding agent that runs inside strangers' repositories now has a public, unpatched command-execution bug and no visible response.
What to do
- Before starting Aider in a repo you didn't write, open
.aider.conf.ymlat its root and checknotifications-commandandeditor. Delete the file or those keys if you don't trust them. - Run coding agents on untrusted code in a container or VM, not on the machine that holds your keys.
- If you build an agent: treat any config that ships inside a repo as untrusted input, and ask before honoring keys that run commands.
- Watch issue #5885 (opens in a new tab) for a fix.
We read the CVE record, the GitHub issue and Aider's source and git history at v0.86.2. We did not run the exploit ourselves.
Sources
- CVE-2026-115726: Aider through 0.86.2 Command Execution via Repository .aider.conf.yml Settings (published Oct 23, 2026)
CVE Program (CNA: VulnCheck)
- Arbitrary Command Execution in Aider via Auto-Loaded .aider.conf.yml Command Keys (issue #5885, Oct 20, 2026)
GitHub
- feat: Add notifications-command option to run custom notification commands (commit 65e059a7, Mar 6, 2025)
GitHub
- refactor: Update subprocess call to use shell=True with properly quoted command string (commit 3714d554, Feb 24, 2025)
GitHub
- Git integration: how Aider marks the commits it authors
Aider
- Aider release history (v0.76.0: "Aider wrote 85% of the code in this release")
Aider
FREE · EVERY WEEK
The top AI tools this week, tested.
Every week MODEL's editors pick the AI tools worth your time, try them hands-on, and tell you what's good, what's not, and who it's for. Free, in your inbox.
Free. Unsubscribe anytime. Our picks are editorial and can't be bought.
The weekly three is editorial. A subscription does not buy a place in it.
Continue
Tech
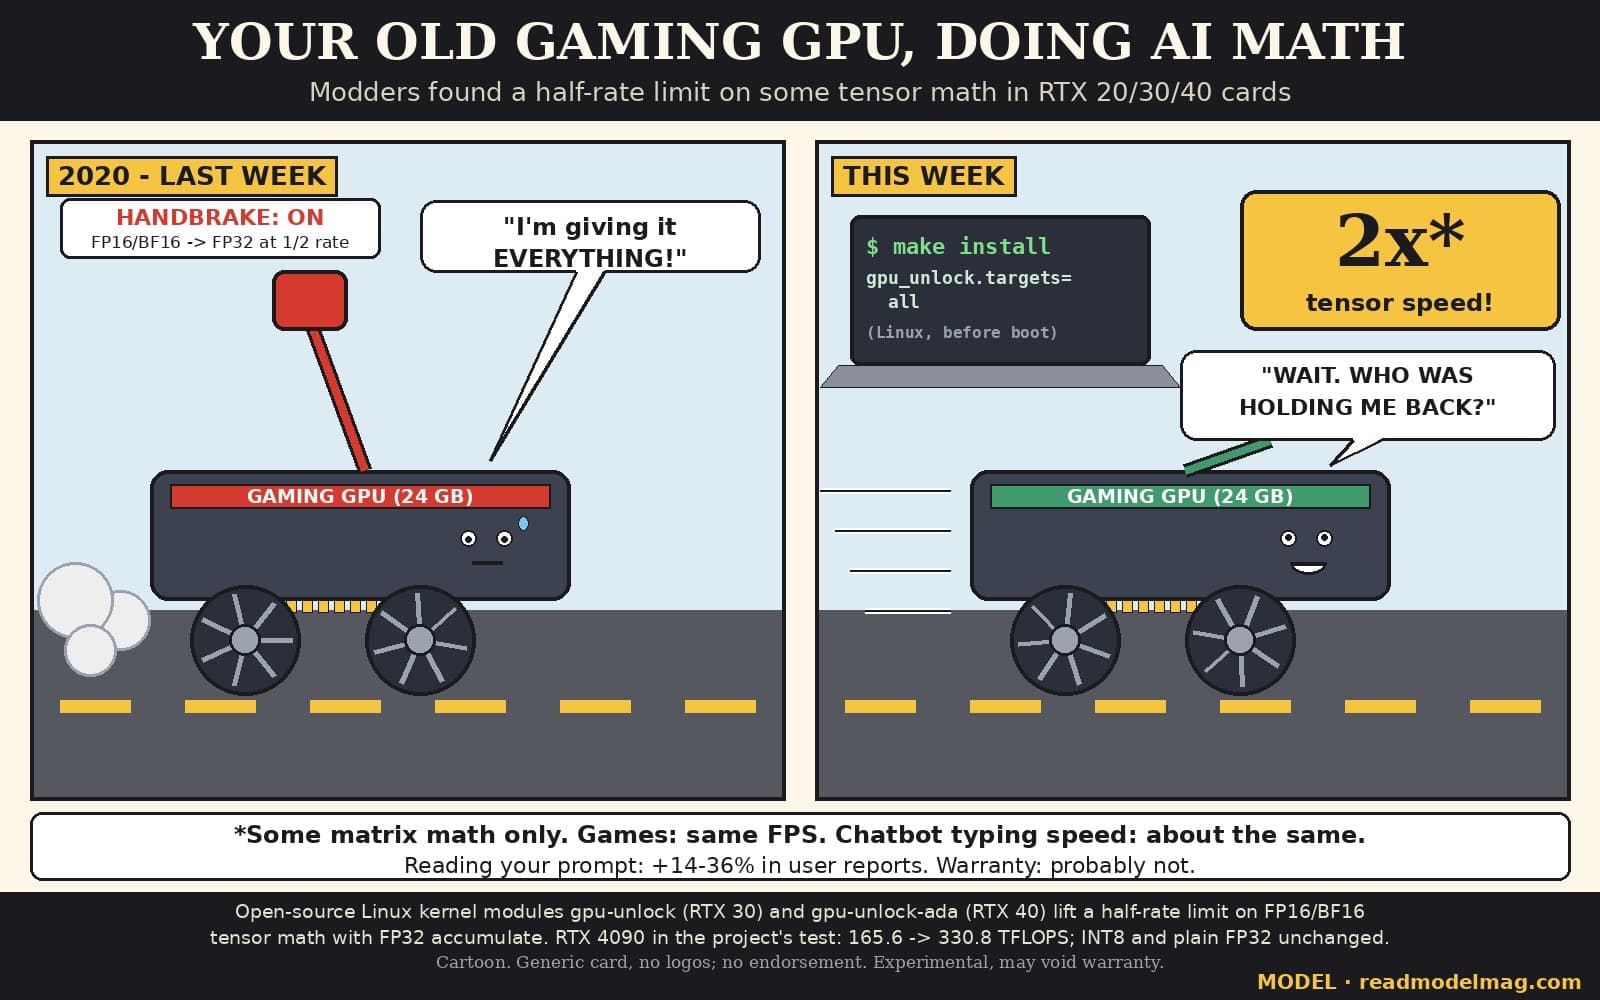
Your old gaming GPU was doing AI math with the handbrake on
Open-source Linux kernel modules lift a half-rate limit on one kind of tensor math in GeForce RTX 20, 30 and 40 cards. An RTX 4090 doubles in that test, from 165.6 to 330.8 TFLOPS. Your games and your chatbot's typing speed stay about the same.
· MODEL Editors
Tech
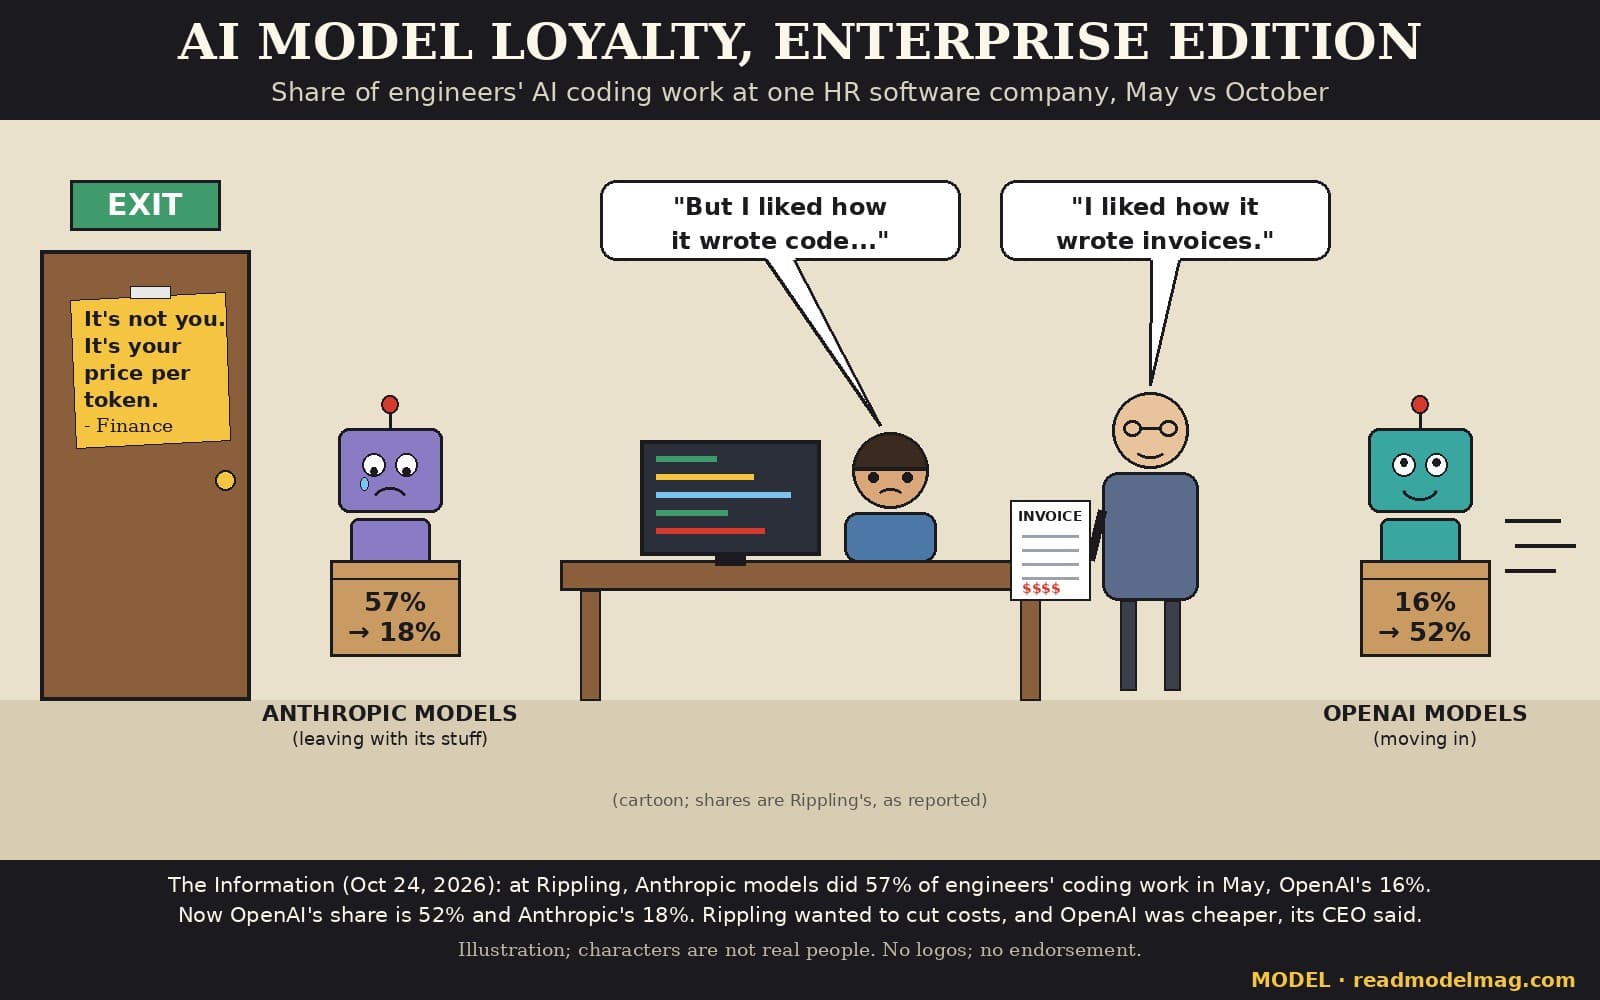
AI model loyalty, enterprise edition: it's not you, it's your price per token
At Rippling, Anthropic models went from doing 57% of engineers' coding work in May to 18%, while OpenAI's share rose from 16% to 52%, The Information reports. The reason its CEO gave: Rippling wanted to cut costs, and OpenAI was cheaper.
· MODEL Editors
Hot take
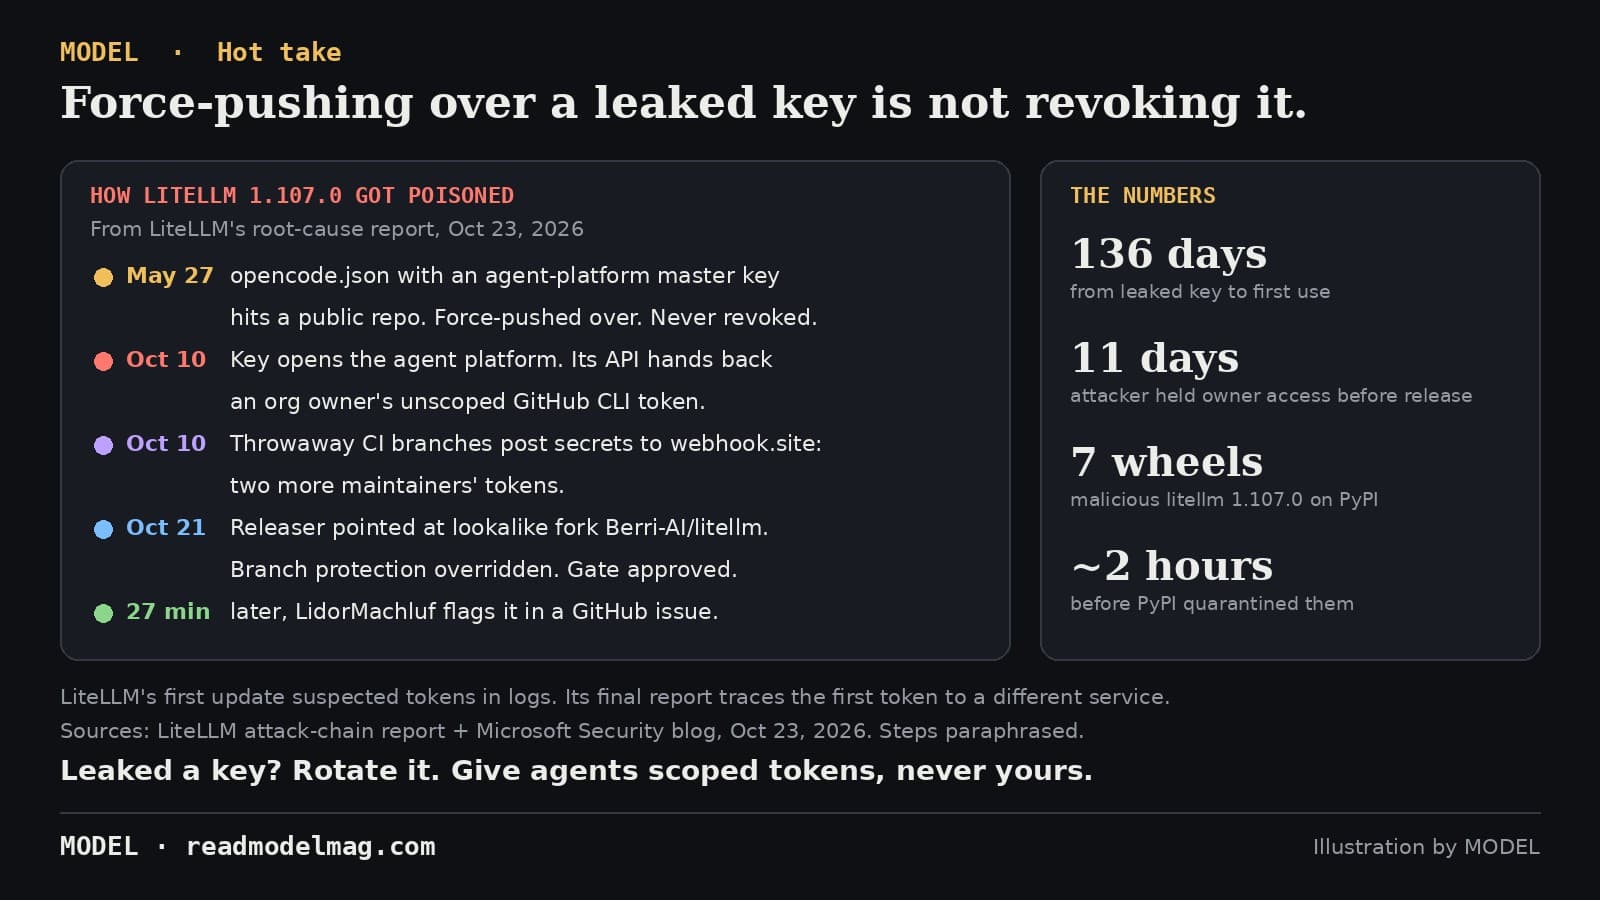
The LiteLLM hack started with a coding-agent config file. The leaked key was force-pushed over, never revoked.
LiteLLM's October 23 root-cause report traces the poisoned 1.107.0 release back to an opencode.json file committed to a public repo on May 27. It held the master key to an internal agent platform, and that platform held an organization owner's unscoped GitHub CLI token. The key sat live for 136 days before anyone used it.
· MODEL Editors