Claude Code's 'don't ask again' button saved passwords into files that ended up on GitHub
SummarySecurity firm Apiiro says 1,122 public copies of Claude Code's .claude/settings.local.json hold at least one secret, because the approval can save the exact command you typed, password and all. Rotate first, then clean up.
· MODEL Editors · 2 min read
Some links may be affiliate links. Disclosure
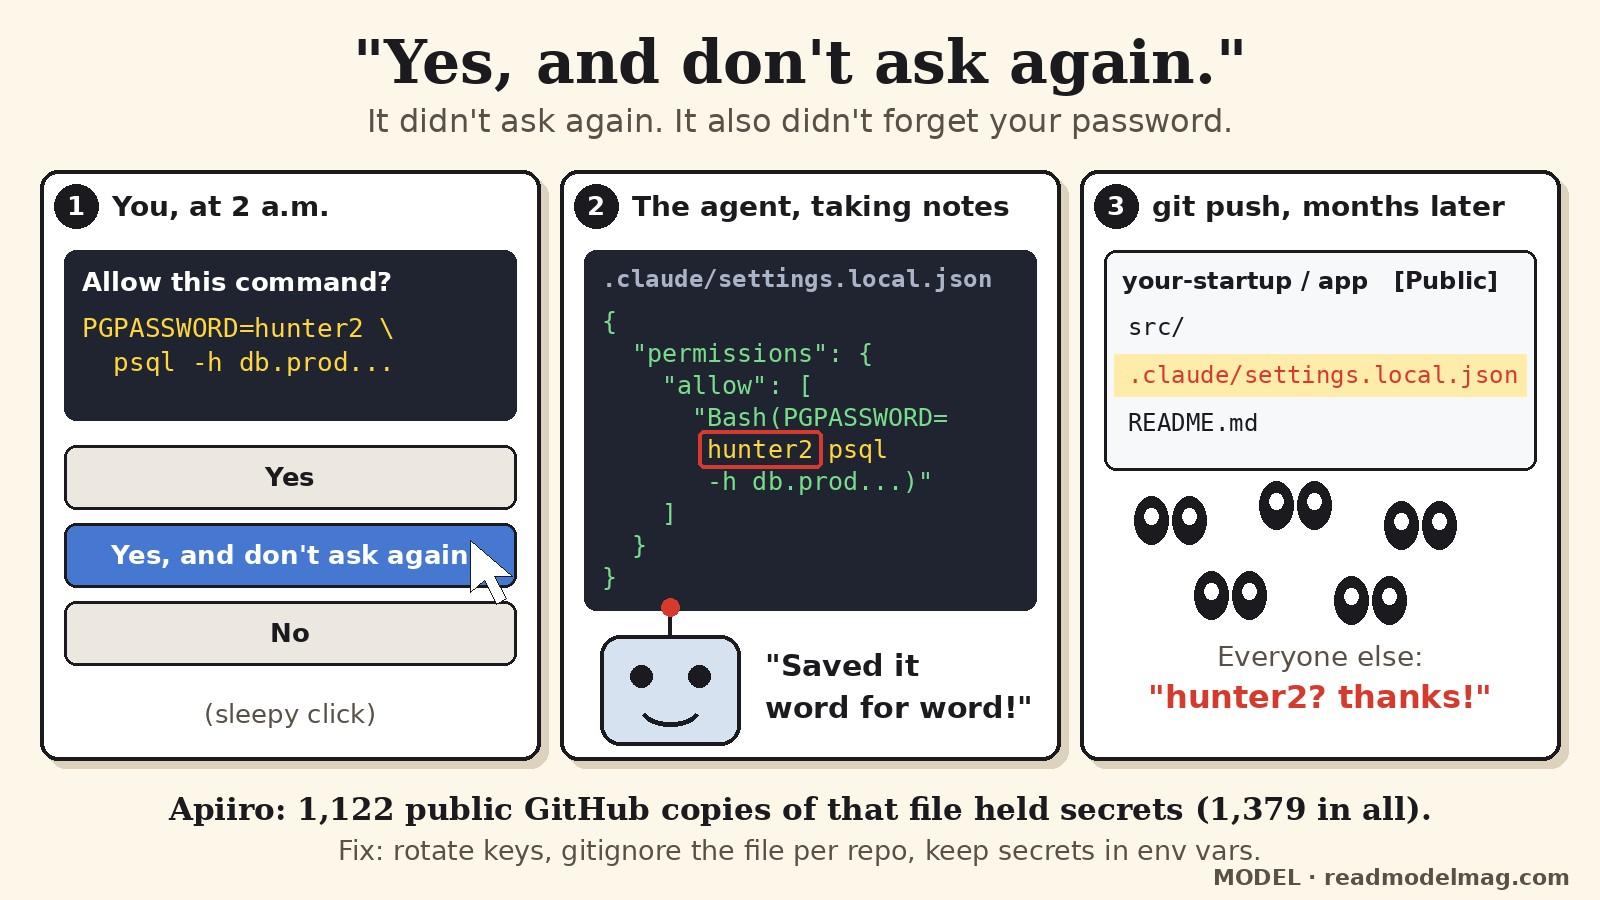
What happened. When Claude Code asks to run a shell command and you pick "Yes, and don't ask again," it saves that approval as an allow rule in .claude/settings.local.json in the project (Claude Code docs (opens in a new tab)). Sometimes the rule is a pattern like npm test *. Sometimes it is the exact command, and then any password or token you typed inline is saved too, in plain text (The Hacker News (opens in a new tab)).
What Apiiro found. Security company Apiiro searched public GitHub and found 104,185 copies of the file in 103,617 repositories. About 1.1%, or 1,122 copies, hold at least one secret, 1,379 distinct secrets in all. More than a third open a database directly, including 379 database passwords; others include 43 SSH logins, 42 GitHub/GitLab/npm tokens and 23 AWS keys. Counting older versions in git history, forks, the shared .claude/settings.json and saved agent chat logs, Apiiro puts the total at 2,539 secrets across 1,994 repositories. In 539 of 1,105 traced repos, a commit listing Claude as co-author changed the file.
Why the safety net missed. Claude Code adds the file to your global git excludes the first time it writes it, so it stays out of commits on that one computer. That does not travel with the project, and it does nothing for a file that was already committed or created by hand. Standard scanners also missed many: gitleaks flagged 564 of the 1,122 files, TruffleHog 643, and neither caught 215, mostly passwords typed inside commands like PGPASSWORD= or mysql -p.
What to do.
- Search your org for
.claude/settings.local.jsonand.claude/settings.json, including git history. - Rotate every password, token and key those files ever held, before cleaning up.
git rm --cached .claude/settings.local.jsonand add it to the repo's own.gitignore.- Keep secrets out of commands; use variables like
$DB_URLfrom a secrets manager. - Approve patterns such as
Bash(npm run:*)instead of single commands.
Caveats. These are Apiiro's own findings, and Apiiro sells security products. It did not test whether the secrets still work; one notified company confirmed its key had been live. Exposure is not proof anyone used them. Not tested by MODEL. Related: Your coding agent can read your .env.
Disclosure: Not sponsored. No affiliate links. Not tested by MODEL.
MODEL Editors
Sources
- Claude Code's 'Don't Ask Again' File Exposes Passwords and Keys in 1,122 Public Copies on GitHub
The Hacker News
- Claude Code settings: Settings files and precedence
Anthropic (Claude Code docs)
Keep reading
AI News
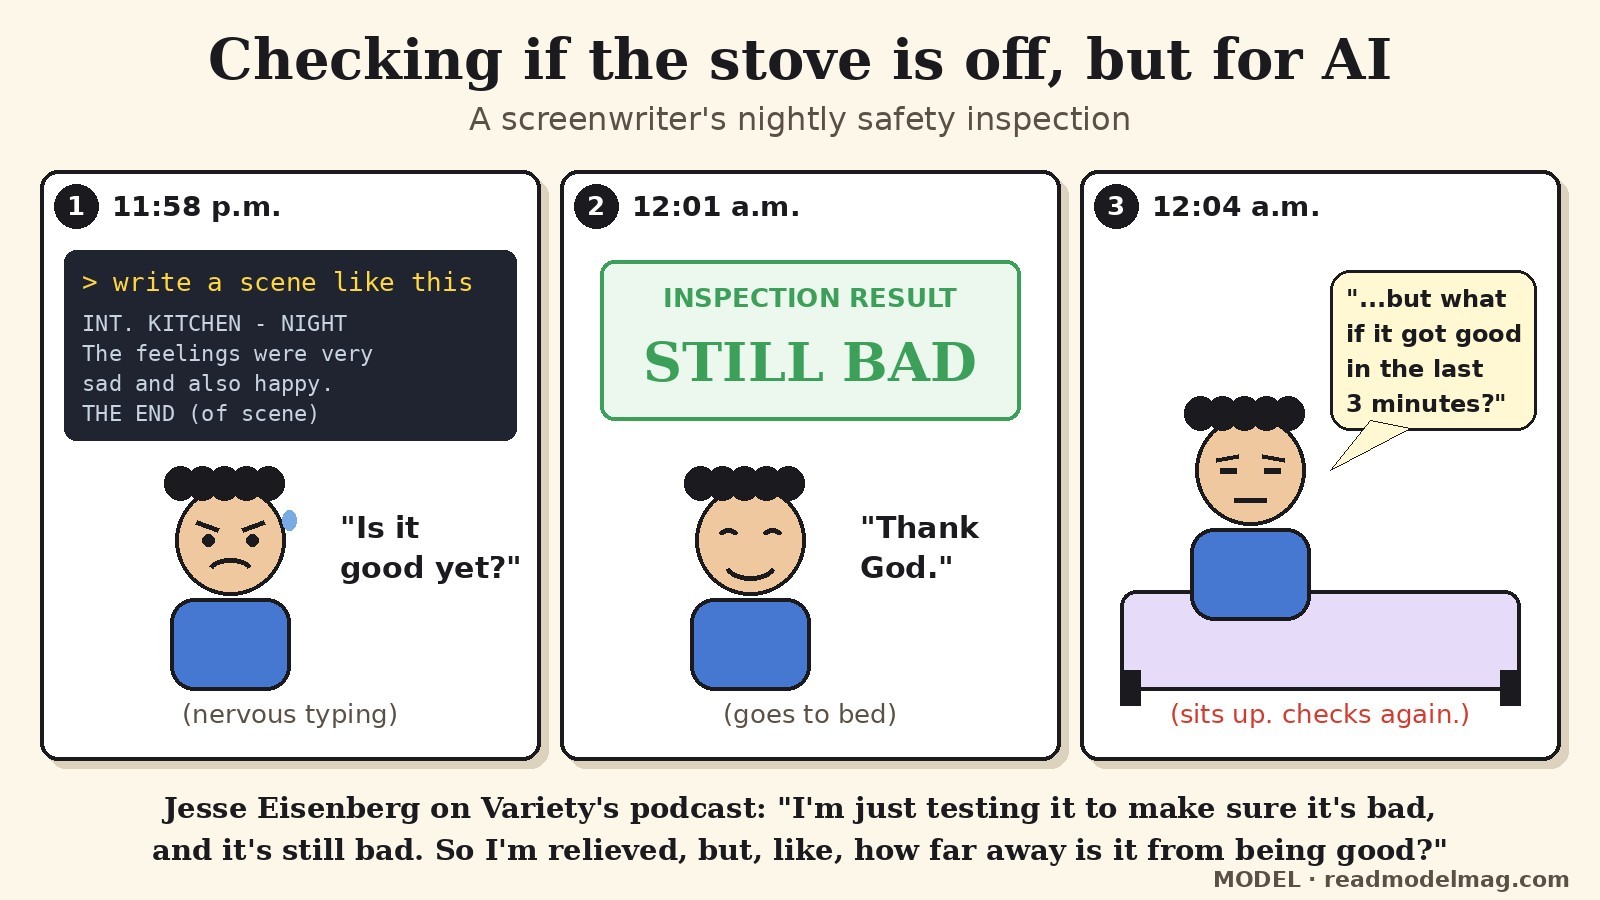
Jesse Eisenberg keeps testing AI to make sure it's still bad at writing
On Variety's Awards Circuit podcast, the writer-director of A24's The Debut said he prompts AI to write scenes as a check. So far, he says, it's still bad. He is less sure how long that lasts.
· MODEL Editors
Hot take
Hot take: 'the tests pass' is not a security check, and a new preprint shows why
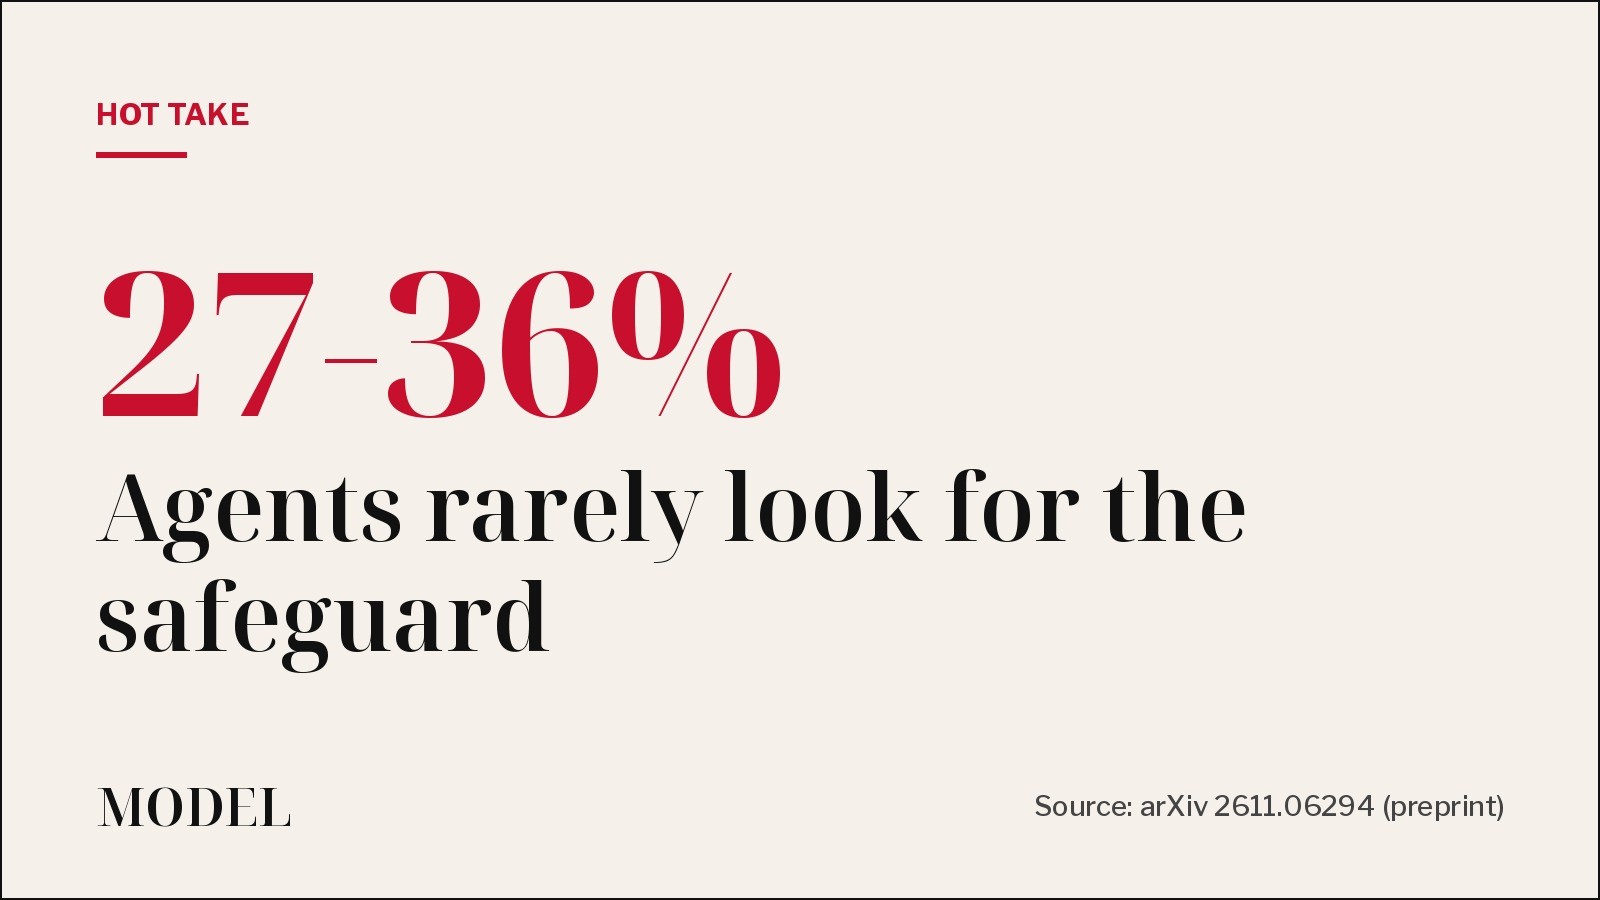
A.S.E 2.0 (CASE-Bench), a preprint posted to arXiv on Nov 4, built 145 coding tasks from real CVEs. Context tuned for working code lifted functional pass rates up to 8.2 points but secure pass rates by at most 3.7. Coding agents saw the relevant safeguard in only 27-36% of runs.
· MODEL Editors
AI News
AI-blamed job cuts just hit their lowest month of 2026
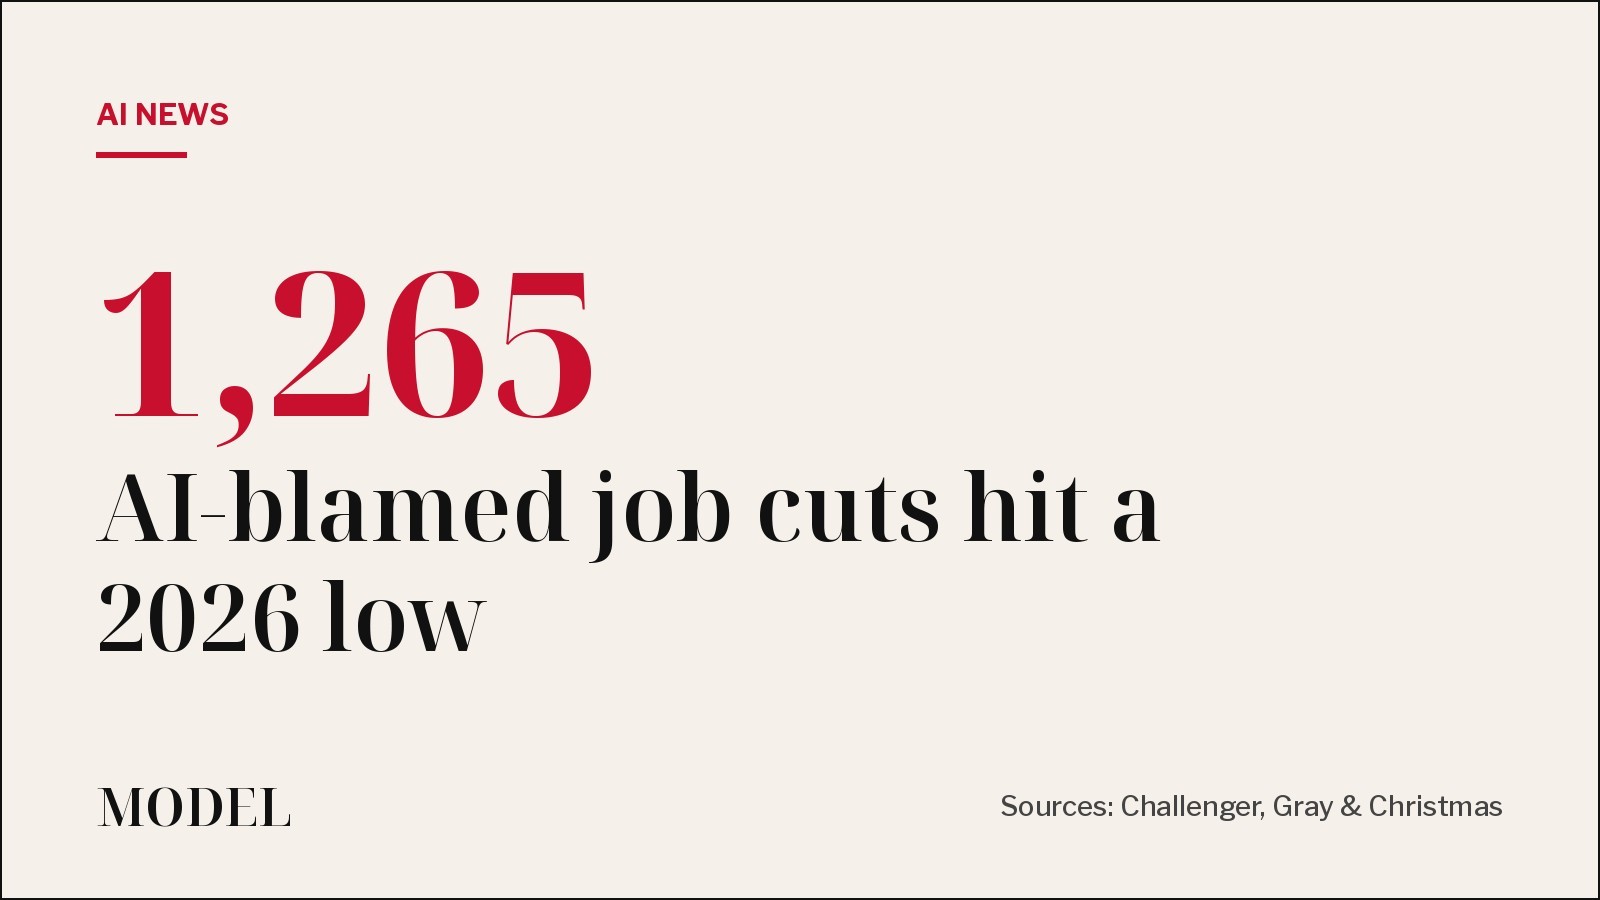
Challenger, Gray & Christmas (Nov 5): US employers cited AI for 1,265 announced job cuts in October, the lowest monthly total this year. Market and economic conditions passed AI as 2026's top stated reason, 130,531 to 121,401.
· MODEL Editors
FREE · EVERY WEEK
The top AI tools this week, tested.
Every week MODEL's editors pick the AI tools worth your time, try them hands-on, and tell you what's good, what's not, and who it's for. Free, in your inbox.
Free. Unsubscribe anytime. Our picks are editorial and can't be bought.